Blog is moving

My blog is moving to http://victormendonca.com/blog/. If you are looking for a specific or older post you are in the right place Otherwise check out my new page for more up to date content.
Showing posts with label DD-WRT. Show all posts

Monday, October 21, 2013

Email DD-WRT Usage Based on MAC Address

If you have limited bandwidth with your ISP and need to monitor data usage of a device at home, here's a neat script that will do just that for you.

The script can check the last day or hour usage and compare with a limit that you set. If it's over it will send you an email with a warning and the amount of data used.

You will need to have the following installed on you DD-WRT router:
. bc (calculation)
. msmtp (email)

The following needs to be changed on the script:

# Change this as needed
SUBJECT=""
MAIL_FROM="[mail address used to send the email]"
MAIL_TO="[the email address we are sending the alert]"
MAIL_FROM_NAME="[mail address used to send the email]"
DAILY_LIMIT="[daily limit for the device]"
HOUR_LIMIT="[hour limit for the device]"
export LD_LIBRARY_PATH="[login to the router and run 'echo $LD_LIBRARY_PATH']"

Copy the script over to your USB on your router, then set two cron jobs in "Administration => Management" using the router's web page:

0 0 * * * root [path]/bandwUsageByMac.sh [YAMon data path] [mac] day >> /jffs/var/log/cron 2>&1
0 * * * * root [path]/bandwUsageByMac.sh [YAMon data path] [mac] hour >>/jffs/var/log/cron 2>&1

And here's the script:

Download

#!/bin/sh
################################################################################
################################################################################
# Name:   bandwUsageByMac.sh
# Usage:  bandwUsageByMac.sh [yamon data folder] [mac] [hour|day]
# Created:  2013-10-17
# Last Modified:
# Copyright 2009, Victor Mendonca - http://wazem.org
# License: Released under the terms of the GNU GPL license
################################################################################
################################################################################

#-------------------------------------------------------------------------------
# Sets variables
#-------------------------------------------------------------------------------

RUN_FOLDER="$1" # Usually /opt/YAMON/data
MAC="$2"
MODE="$3"
USAGE="Usage: bandwUsageByMac.sh [yamon data folder] [mac] [hour|day]
"
HOUR=$(date +%H)
DATE=$(date +%d-%m-%Y)
YESTERDAY=$(awk -v days="-1" 'BEGIN{print \
strftime("%d",systime()+(days*86400))}')
LAST_HOUR=$(awk -v hour="-1" 'BEGIN{print \
strftime("%H",systime()+(hour*3600))}')

# Change this as needed
SUBJECT="DD-WRT Usage"
MAIL_FROM=""
MAIL_TO=""
MAIL_FROM_NAME=""
DAILY_LIMIT="1024"
HOUR_LIMIT="250"
export LD_LIBRARY_PATH=""

#-------------------------------------------------------------------------------
# Functions
#-------------------------------------------------------------------------------

SendMail () {
## Example command
# echo "$VAR1" | msmtp -C msmtprc user@domain.com

## Example Body
#To: user@domain.com
#FROM: router@home.com
#Subject: DD-WRT - Usage
#This is a test.
#Ciao

MAIL="To: $MAIL_TO
FROM: $MAIL_FROM_NAME
Subject: $SUBJECT
$BODY"

echo "$MAIL" | msmtp -C /jffs/etc/msmtprc $MAIL_TO
}


CalcMB () {
echo "scale=2;(${1}*9.5367)/10000000" | bc
}


## => Daily Usage <= ##
getDayUsage () {
LOG_TOTL=$(ls -tr *mac_data.html | tail -1)
if [ "x$LOG_TOTL" = "x" ] ; then
  echo "Could not find daily usage file"
  exit 1
fi

#-- Daily download
DOWNLOAD_TOTAL=$(grep -i "${MAC}.*${YESTERDAY}$" ${LOG_TOTL} | awk -F, '{print $3}')
if [ "x$DOWNLOAD_TOTAL" = "x" ] ; then
  exit 0
fi
DOWNLOAD_TOTAL=$(CalcMB ${DOWNLOAD_TOTAL})

#-- Daily upload
UPLOAD_TOTAL=0
UPLOAD_TOTAL=$(grep -i "${MAC}.*${YESTERDAY}$" ${LOG_TOTL} | awk -F, '{print $4}')
UPLOAD_TOTAL=$(echo "scale=2;(${UPLOAD_TOTAL}*9.5367)/10000000" | bc)
DAILY_TOTAL=$(echo ${DOWNLOAD_TOTAL} + ${UPLOAD_TOTAL} | bc)
if [[ $(echo "$DAILY_TOTAL $DAILY_LIMIT" | awk '{if ($1 > $2) print "1"; else print "0";}') -eq 1 ]] ; then
  BODY="
Total day usage has gone over limit of ${DAILY_LIMIT}MB

DOWN: ${DOWNLOAD_TOTAL}MB UP: ${UPLOAD_TOTAL}MB
TOTAL: ${DAILY_TOTAL}MB"
  SendMail
else
  echo "Usage ok"
fi

echo "TOTAL - DOWN: $DOWNLOAD_TOTAL UP: $UPLOAD_TOTAL"
}


## => Hour Usage <= ##
getHourUsage () {
LOG_HOUR="${DATE}-hourly_data.html"
if [ "x$LOG_HOUR" = "x" ] ; then
  echo "Could not find hour usage file"
  exit 1
fi

#-- Hourly download
DOWNLOAD_HOUR=$(grep -i "${MAC}.*${LAST_HOUR}$" ${LOG_HOUR} | awk -F, '{print $3}')
if [ "x$DOWNLOAD_HOUR" = "x" ] ; then
  echo "No hourly file"
  exit 0
fi
DOWNLOAD_HOUR=$(echo "scale=2;(${DOWNLOAD_HOUR}*9.5367)/10000000" | bc)

#-- Hourly upload
UPLOAD_HOUR=$(grep -i "${MAC}.*${LAST_HOUR}$" ${LOG_HOUR} | awk -F, '{print $4}')
UPLOAD_HOUR=$(echo "scale=2;(${UPLOAD_HOUR}*9.5367)/10000000" | bc)

HOUR_TOTAL=$(echo ${DOWNLOAD_HOUR} + ${UPLOAD_HOUR} | bc)
if [[ $(echo "$HOUR_TOTAL $HOUR_LIMIT" | awk '{if ($1 > $2) print "1"; else print "0";}') -eq 1 ]] ; then
  BODY="
Total hour usage has gone over limit of ${HOUR_LIMIT}MB

DOWN: ${DOWNLOAD_HOUR}MB UP: ${UPLOAD_HOUR}MB
TOTAL: ${HOUR_TOTAL}MB"
  SendMail
else
  echo "Usage ok"
fi

echo "Hour - DOWN: $DOWNLOAD_HOUR UP: $UPLOAD_HOUR"
}

#-------------------------------------------------------------------------------
# Starts script
#-------------------------------------------------------------------------------

if [[ $# -ne 3 ]] ; then
  echo $USAGE
  exit 1
fi

if [[ $(cd "$RUN_FOLDER" 2> /dev/null ; echo $?) -eq 0 ]] ; then
  cd "$RUN_FOLDER"
else
  echo "yamon data folder could not be found"
  exit 1
fi

case $MODE in
 day) getDayUsage ;;
 hour) getHourUsage ;;
 *) echo "$USAGE" 
    exit 1 ;;
esac

Friday, October 18, 2013

How to install packages on Asus RT-AC66U with DD-WRT (opkg)

If you are having issues installing packages with the built-in ipkg, this post might help you. Please note that the links that I provide are hardware specific, so you need to find what your hardware is and then find the proper download path here - http://downloads.openwrt.org/attitude_adjustment/12.09/.

Before we start, let's make sure your USB is working. Make sure it's formatted with ext3.

=> 1- USB Setup

1a. Login to your router and go to Services => USB:


1b. Make sure that these options are enabled:
- Core USB Support
- USB Storage Support
- Automatic Drive Mount

1c. Connect to your router via ssh and plug in your USB; then run the command "df -h"

# df -h
 Filesystem                Size      Used Available Use% Mounted on
 rootfs                   16.0M     16.0M         0 100% /
 /dev/root                16.0M     16.0M         0 100% /
 none                    512.0K         0    512.0K   0% /dev
 /dev/sda1               464.9M     0    464.9M   0% /tmp/mnt/sda1

My USB drive shows as '/dev/sda1' mounted in '/tmp/mnt/sda1'

1d. Create a /opt and /jffs on your USB drive

# mkdir /tmp/mnt/sda1/opt /tmp/mnt/sda1/jffs

1e. Back to your router admin page, go to Administration => Commands. Add a startup command with the following code:

 ## Sets up USB mount
 CURRENT_MOUNT=$(df -h | grep sda | awk '{print $6}')
 umount $CURRENT_MOUNT
 mount /dev/sda1 /mnt
 mount -o bind /mnt/opt /opt
 mount -o bind /mnt/jffs /jffs

Note: the command above assumes you have only one USB device and it shows as /dev/sda*

1f. Reboot the router

# reboot

1g. Logon via ssh again and check the mount points

 # df -h
 Filesystem                Size      Used Available Use% Mounted on
 rootfs                   16.0M     16.0M         0 100% /
 /dev/root                16.0M     16.0M         0 100% /
 none                    512.0K         0    512.0K   0% /dev
 /dev/sda1               464.9M     0    464.9M   0% /tmp/mnt
 /dev/sda1               464.9M     0    464.9M   0% /opt
 /dev/sda1               464.9M     0    464.9M   0% /jffs

=> 2- Install opkg

2a. First let's update the ipkg package list

# ipkg update

2b. Now let's install opkg to '/jffs'

# ipkg -d /jffs install http://downloads.openwrt.org/attitude_adjustment/12.09/brcm47xx/generic/packages/opkg_618-3_brcm47xx.ipk 

2c. Set 'dest root' in '/jffs/etc/opkg.conf' to use '/jffs'

# cat /jffs/etc/opkg.conf
src/gz attitude_adjustment http://downloads.openwrt.org/attitude_adjustment/12.09/brcm47xx/generic/packages
dest root /jffs
dest ram /tmp
lists_dir ext /var/opkg-lists
option overlay_root /overlay 

2d. Update opkg

# opkg -f /jffs/etc/opkg.conf update

2e. Install libc (dependency)

# opkg -f /jffs/etc/opkg.conf install http://downloads.openwrt.org/attitude_adjustment/12.09/brcm47xx/generic/packages/libc_0.9.33.2-1_brcm47xx.ipk

2f. Now you can install packages with

# opkg -f /jffs/etc/opkg.conf install [package]

Monday, October 14, 2013

How to install DD-WRT on Asus RT-AC66U (AC1750)

Update (Oct 23 2014)

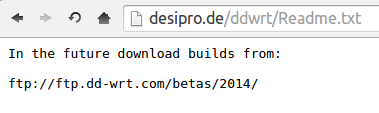
It looks like the link for Kongs build is down (.bin file), and his images are now being posted under the "betas" ftp site for DD-WRT:


My instructions show how to install the stable (at that time) DD-WRT version from BrainSlayer, and then flash Kong's firmware, which usually has additional options.

If you just to want to install DD-WRT, I think the best option would be to follow the instructions on the official wiki - http://www.dd-wrt.com/wiki/index.php/Asus_RT-AC66U.

If you want to install Kong's firmware, go to the link he mentioned (screenshot above) and look for the folder "asus-rt-ac66u". These are all beta and might have images from other contributors.

Please note that I followed the procedure I outlined below, but I believe that flashing from the official wiki should be pretty safe.

-----------------------------------------------------------------------------------------------------------------

Here are quick instructions on how to install DD-WRT in the new Asus RT-AC66U. You can find additional info and get support here.

You are going to need two files; the first is a .trx, and the second is a .bin.

Download trx
Download bin

1- Login via UI and enable telnet (or ssh)

2- Login via telnet (or ssh)

$ telnet 192.168.1.1
Trying 192.168.1.1...
Connected to 192.168.1.1.
Escape character is '^]'.
RT-AC66U login: admin
Password: 


ASUSWRT RT-AC66U_3.0.0.4 Fri Jul  5 03:20:20 UTC 2013
admin@RT-AC66U:/tmp/home/root#

3- Clear the nvram with 'mtd-erase -d nvram':


# mtd-erase -d nvram
Erasing 0x0 - 0xffff
"nvram" successfully erased.

4- Reboot the router


# reboot
Rebooting...
admin@RT-AC66U:/tmp/home/root# Connection closed by foreign host.

5- Login via UI (password is reset to admin:admin)

6- Install the .trx file

7- Login via telnet again


$ telnet 192.168.1.1
Trying 192.168.1.1...
Connected to 192.168.1.1.
Escape character is '^]'.

DD-WRT v24-sp2 giga (c) 2013 NewMedia-NET GmbH
Release: 07/24/13 (SVN revision: 22118)

DD-WRT login: root
Password: 
==========================================================

 ____  ___    __        ______ _____         ____  _  _ 
 | _ \| _ \   \ \      / /  _ \_   _| __   _|___ \| || | 
 || | || ||____\ \ /\ / /| |_) || |   \ \ / / __) | || |_ 
 ||_| ||_||_____\ V  V / |  _ < | |    \ V / / __/|__   _| 
 |___/|___/      \_/\_/  |_| \_\|_|     \_/ |_____|  |_| 

                       DD-WRT v24-sp2
                   http://www.dd-wrt.com

==========================================================


BusyBox v1.21.0 (2013-07-24 10:53:52 CEST) built-in shell (ash)
Enter 'help' for a list of built-in commands.

root@DD-WRT:~#

8- Erase nvram again, this time include 'clear nvram'


# mtd-erase -d nvram
Erasing 0x0 - 0xffff
"nvram" successfully erased.

# clear nvram

9- Reboot the router


# reboot
root@DD-WRT:~# Connection closed by foreign host.

10- Login via UI and install the *.bin file

Tuesday, July 30, 2013

How to Browse Securely on Your Android

If you are not aware of the risks of accessing your online accounts, like email or Facebook, when connecting to your local coffee shop open Wi-Fi, well here are some news... You definitely should! Any open Wi-Fi (the ones that don’t require password) are dangerous as they allow other people connected to the same Wi-Fi to “eavesdrop” on your connection. They can see what sites you are accessing, and sometimes even hijack your session and login to your account (yes, login to your Facebook as if they were you). PC World has a great article on how easy this can be done.
Here's what an eavesdropper sees when you use an unsecured Wi-Fi hotspot
Securing your browsing is not that difficult and it’s something that can be done even by the non technical user, however it usually requires that your Android phone is rooted (which is really just obtaining administrator access to your phone). I will provide some options, however I’m not going into details on how to configure them. There are plenty of tutorials online for that.


=> Using a proxy server with ProxyDroid

https://play.google.com/store/apps/details?id=org.proxydroid

ProxyDroid will connect to a proxy server (Wikipedia) somewhere on the Internet and send all your connection (traffic) trough that server. It’s somewhat similar to using a broker to buy insurance (the picture below, from Wikipedia, will give you a better idea).


You can find free proxy servers and accounts here - http://free.billproxy.com/


=> Using tor with Orbot


https://play.google.com/store/apps/details?id=org.torproject.android

Tor (Wikipedia) is a technology that allows you to connect to other computers so you can browse anonymously. This is something that a lot of hackers use to stay anonymous, and of course it’s also a great way to protect your data while browsing.


=> Using OpenVPN


https://play.google.com/store/apps/details?id=de.blinkt.openvpn

OpenVPN is a open source VPN (Wikipedia) software that works with multi-platform (Linux, Windows, Android, routers, etc...). It’s similar to a proxy server, however you connect to your computer at home so you can browse safely from there.


I have posted instructions previously on how to configure OpenVPN with Android and a DD-WRT router - How To Configure OpenVPN between DD-WRT, Ubuntu and Android


Monday, July 29, 2013

How To Configure OpenVPN between DD-WRT, Ubuntu and Android

This guide you walk you trough setting up OpenVPN between you DD-WRT router, a laptop and a rooted Android phone so you can connect to home resources, or browse safer while on open networks, like an internet cafe.

Setting up OpenVPN is not that hard, however you may run into issues, so be patient. You will need a CA server to sign the certificates. But don't worry, any Linux machine can do that. However I would advise against doing it on the laptop that you will be using to connect remotelly in case it gets stolen or hacked.

I'm going to start with the CA server, which for me is really just a desktop at home with Ubuntu 12.04.


=> Generating the keys

1- Install OpenVPN and the OpenVPN ui for network manager

$ sudo apt-get install openvpn network-manager-openvpn

2- Copy the easy-rsa directory to /etc/ so it doesn't get overwritten on system updates

$ sudo -i
# mkdir /etc/openvpn/easy-rsa 
# cp -r /usr/share/doc/openvpn/examples/easy-rsa/2.0/* /etc/openvpn/easy-rsa/. 

3- Edit the vars file with the parameters that you would like to use for your OpenVPN certificates. The next commands will use the variables we set here to create the certificates

# cd /etc/openvpn/easy-rsa/ 
# vim vars 

KEY_COUNTRY= "[Two digit country. I used CA for Canada]"
KEY_PROVINCE="[Two digit province]"
KEY_CITY="[City, e.g.: Toronto]"
KEY_ORG="[Company name]" 
KEY_EMAIL="[Your email address]" 
KEY_EMAIL=[Your email address without double quotes]

4- Export variables by sourcing 'vars'

# . vars

In case you get the following error

************************************************************** 
  No /etc/openvpn/easy-rsa/openssl.cnf file could be found 
  Further invocations will fail 
************************************************************** 

Check your version of ssl

$ dpkg -s openssl | grep Version 
Version: 1.0.1-4ubuntu5.8

Then check what version is in the folder

$ ll openssl* 
-rw-r--r-- 1 root root 7.6K Apr  8 17:34 openssl-0.9.6.cnf 
-rw-r--r-- 1 root root 8.2K Apr  8 17:34 openssl-0.9.8.cnf 
-rw-r--r-- 1 root root 8.1K Apr  8 17:34 openssl-1.0.0.cnf 
-rw-r--r-- 1 root root 8.1K Apr  8 17:34 openssl-1.0.0.cnf-old-copy

Create a symbolic link to use the version in the folder that is the closest to yours

# ln -s openssl-1.0.0.cnf openssl.cnf

And now try to source 'vars' again

# . vars
NOTE: If you run ./clean-all, I will be doing a rm -rf on /etc/openvpn/easy-rsa/keys

5- Delete old keys by running clean-all

# ./clean-all

6- Generate the CA keys with build-ca. The parameters that we entered in 'vars' will be populated here, all you have to do is hit enter.

# ./build-ca
Generating a 1024 bit RSA private key
...............++++++
.......++++++
writing new private key to 'ca.key'
-----
You are about to be asked to enter information that will be incorporated
into your certificate request.
What you are about to enter is what is called a Distinguished Name or a DN.
There are quite a few fields but you can leave some blank
For some fields there will be a default value,
If you enter '.', the field will be left blank.
-----
Country Name (2 letter code) [CA]:
State or Province Name (full name) [ON]:
Locality Name (eg, city) [Toronto]:
Organization Name (eg, company) [Wazem]:
Organizational Unit Name (eg, section) [changeme]:
Common Name (eg, your name or your server's hostname) [changeme]:DD-WRT
Name [changeme]:
Email Address [victor@xxxx.com]:

7- You should now be able to see the keys

# ll keys/
total 20
drwx------ 2 root root 4096 Apr  8 17:53 ./
drwxr-xr-x 4 root root 4096 Apr  8 17:54 ../
-rw-r--r-- 1 root root 1342 Apr  8 17:53 ca.crt
-rw------- 1 root root  912 Apr  8 17:53 ca.key
-rw-r--r-- 1 root root    0 Apr  8 17:52 index.txt
-rw-r--r-- 1 root root    3 Apr  8 17:52 serial

8- Now let's create the server keys with './build-key-server [server-name]'. When you are asked to sign and commit the certificate, enter “y”

# ./build-key-server dd-wrt
Generating a 1024 bit RSA private key
....++++++
..++++++
writing new private key to 'dd-wrt.key'
-----
You are about to be asked to enter information that will be incorporated
into your certificate request.
What you are about to enter is what is called a Distinguished Name or a DN.
There are quite a few fields but you can leave some blank
For some fields there will be a default value,
If you enter '.', the field will be left blank.
-----
Country Name (2 letter code) [CA]:
State or Province Name (full name) [ON]:
Locality Name (eg, city) [Toronto]:
Organization Name (eg, company) [Wazem]:
Organizational Unit Name (eg, section) [changeme]:
Common Name (eg, your name or your server's hostname) [dd-wrt]:
Name [changeme]:
Email Address [victor@xxxx.com]:

Please enter the following 'extra' attributes
to be sent with your certificate request
A challenge password []:
An optional company name []:Wazem
Using configuration from /etc/openvpn/easy-rsa/openssl.cnf
Check that the request matches the signature
Signature ok
The Subject's Distinguished Name is as follows
countryName           :PRINTABLE:'CA'
stateOrProvinceName   :PRINTABLE:'ON'
localityName          :PRINTABLE:'Toronto'
organizationName      :PRINTABLE:'Wazem'
organizationalUnitName:PRINTABLE:'changeme'
commonName            :PRINTABLE:'dd-wrt'
name                  :PRINTABLE:'changeme'
emailAddress          :IA5STRING:'victor@xxxx.com'
Certificate is to be certified until Apr  6 22:02:04 2023 GMT (3650 days)
Sign the certificate? [y/n]:y


1 out of 1 certificate requests certified, commit? [y/n]y
Write out database with 1 new entries
Data Base Updated

9- Now let's create a diffie hellman key

# ./build-dh
Generating DH parameters, 1024 bit long safe prime, generator 2
This is going to take a long time
................................................................
....................................+...........................
............................+...................................
................................................................
..........................................................+.....
................................................................
............+..........++*++*++*a

10- And finally the client keys with ./build-key [client.name]

# ./build-key galaxyS3

11- You should see a new key and certificate for the new client. Create as many as you need

# ll galaxy*
total 8.0K
-rw------- 1 root root 3.9K Apr  9 05:30 galaxyS3.crt
-rw------- 1 root root  916 Apr  9 05:30 galaxyS3.key


=> Configure router

1- Open the Admin page of DD-WRT and go to "Services => VPN"


2- Complete the following fields

Start OpenVPN - Enable
Start type - Wan Up
Public Server Cert - Paste the contents of ca.crt
Certificate Revoke List - Leave blank
Public Client Cert - Paste the contents of server.crt
Private Client Key - Paste the contents of server.key
DH PEM - Paste the contents of dh1024.pem
OpenVPN Config - See below
OpenVPN TLS Auth - Leave blank

3- For the OpenVPN config, my example uses the following:
- My router has a LAN IP of 192.168.1.1
- My VPN network will be 192.168.10.0
- I'm using Open DNS as my DNS for the VPN network

push "route 192.168.1.1 255.255.255.0"
server 192.168.10.0 255.255.255.0

push "dhcp-option DNS 208.67.222.222”

dev tun0
proto udp
keepalive 10 120
dh /tmp/openvpn/dh.pem
ca /tmp/openvpn/ca.crt
cert /tmp/openvpn/cert.pem
key /tmp/openvpn/key.pem

# Only use crl-verify if you are using the revoke list, otherwise leave it commented out
# crl-verify /tmp/openvpn/ca.crl

# management parameter allows DD-WRT's OpenVPN Status web page to access the server's management port
# port must be 5001 for scripts embedded in firmware to work
management localhost 5001

Commands
# Opens firewall for incoming port 1194
iptables -I INPUT 1 -p udp --dport 1194 -j ACCEPT

# Allows connection from local VPN to the Internet
iptables -I FORWARD 1 --source 192.168.10.0/24 -j ACCEPT
# Allows connection between the local network and local VPN
iptables -I FORWARD -i br0 -o tun0 -j ACCEPT
iptables -I FORWARD -i tun0 -o br0 -j ACCEPT

4- Click on "Save" and then "Apply"


=> Client Config (Ubuntu 12.10)

1- Install OpenVPN and the OpenVPN ui for network manager

$ sudo apt-get install openvpn network-manager-openvpn

2- Copy the easy-rsa directory to /etc/ so it doesn't get overwritten on system updates

$ sudo -i
# mkdir /etc/openvpn/easy-rsa 
# cp -r /usr/share/doc/openvpn/examples/easy-rsa/2.0/* /etc/openvpn/easy-rsa/. 

3- upload ca.crt to /etc/openvpn and run chmod 600

$ cd /etc/openvpn
# chmod 600 ca.crt
$ ll ca.crt
-rw-r--r-- 1 root root 1.4K Apr  9 05:30 ca.crt

4- Create the client folders

# mkdir -p /etc/openvpn/easy-rsa/keys

5- Upload the client .crt and .key files to /etc/openvpn/easy-rsa/keys and chmod 600

$ cd /etc/openvpn/easy-rsa/keys
# chmod 600 Ubuntu.*
$ $ ll
-rw------- 1 root root 3.9K Apr  9 05:30 Ubuntu.crt
-rw------- 1 root root  916 Apr  9 05:30 Ubuntu.key

6- Open System Settings => Network

7- Click on the plus sign on the bottom


8- Select the "VPN" interface and click on "create"


7- Select "OpenVPN" and click on create


8- Complete the fields below and click on "save"


9- You should now see the VPN connection on your network manager (and it should be working) 


=> Android Config

1- Install OpenVpn for Android


https://play.google.com/store/apps/details?id=de.blinkt.openvpn&hl=en


2- Create a new folder in your sdcard called openvpn


3- Connect to your android and transfer the ca.crt, client.crt and client.key

4- Open OpenVPN for Android and click on the plus sign


5- Enter a name


6- Click on Basic


7- Enter server address; change Type to "Certificates"; select the 3x files that we have uploaded; click back twice


8- You should now be able to establish a VPN connection from your phone.


=> Troubleshooting

Ubuntu Logs
You can monitor /var/log/syslog for messages while attempting to open a connection

Timezone
Check that date and time on router is the same as the computer where you created the keys. For me adding a NTP server on the router and changing it's timezone to UTC with no savings fixed my issues.


Reference:
http://www.techronicles.net/2012/12/openvpn-server-on-ubuntu-1210-with.html
http://www.howtogeek.com/64433/how-to-install-and-configure-openvpn-on-your-dd-wrt-router/
https://help.ubuntu.com/11.10/serverguide/openvpn.html
http://www.dd-wrt.com/wiki/index.php/VPN_(the_easy_way)_v24%2B